Your people
A full, useful answer
Jana Nováková, 41,
62,000 CZK
For regulated and audited companies
Every AI prompt on the audit trail; sensitive data stays in-house.
Your people already paste client and company data into AI tools. ABOS sits between them and the models, records every request, and keeps sensitive data inside the company.
The broker types
Mortgage options for Jana Nováková, 41, net income 62,000 CZK
What leaves the firm
Mortgage options for [CLIENT_1], 40–45, net income 50–75k CZK
The broker reads
The full answer, with Jana Nováková put back in
Example: a broker network, Monday 9:00
“Document every use of AI involving client data by your agents in the last twelve months.”
You are its compliance officer, and you know the answer. Everywhere, and nowhere. Your agents use AI every day, yet there is no record to show.
The request targets the firm, not the agent. The licensed firm answers to the supervisor for every tied agent working under its license.
Swap the regulator for a customer’s auditor, a NIS2 supervisor or your own board. The question stays the same: who used AI on which data, and where did it go?
How it works
ABOS records, sanitizes and sends. Your people keep working with the AI tools they already use.
Inside the company
Every request is tied to a person and written to a tamper-evident log.
Inside the company
Personal and confidential data is swapped for placeholders before anything leaves.
Outside the company
Only placeholders leave, and only to the model providers your policy approves.
Inside the company
The real values are put back into the answer, inside the company.
The log is the product. The gateway just gets you one.
What it delivers
Your people
Jana Nováková, 41,
62,000 CZK
The model
[CLIENT_1], 40–45,
50–75k CZK
The compliance officer
Who asked, what left,
where, in what form
The examples follow the broker from the top of the page.
Your people keep the answer. Your clients keep their privacy. The company keeps the record.
Running today
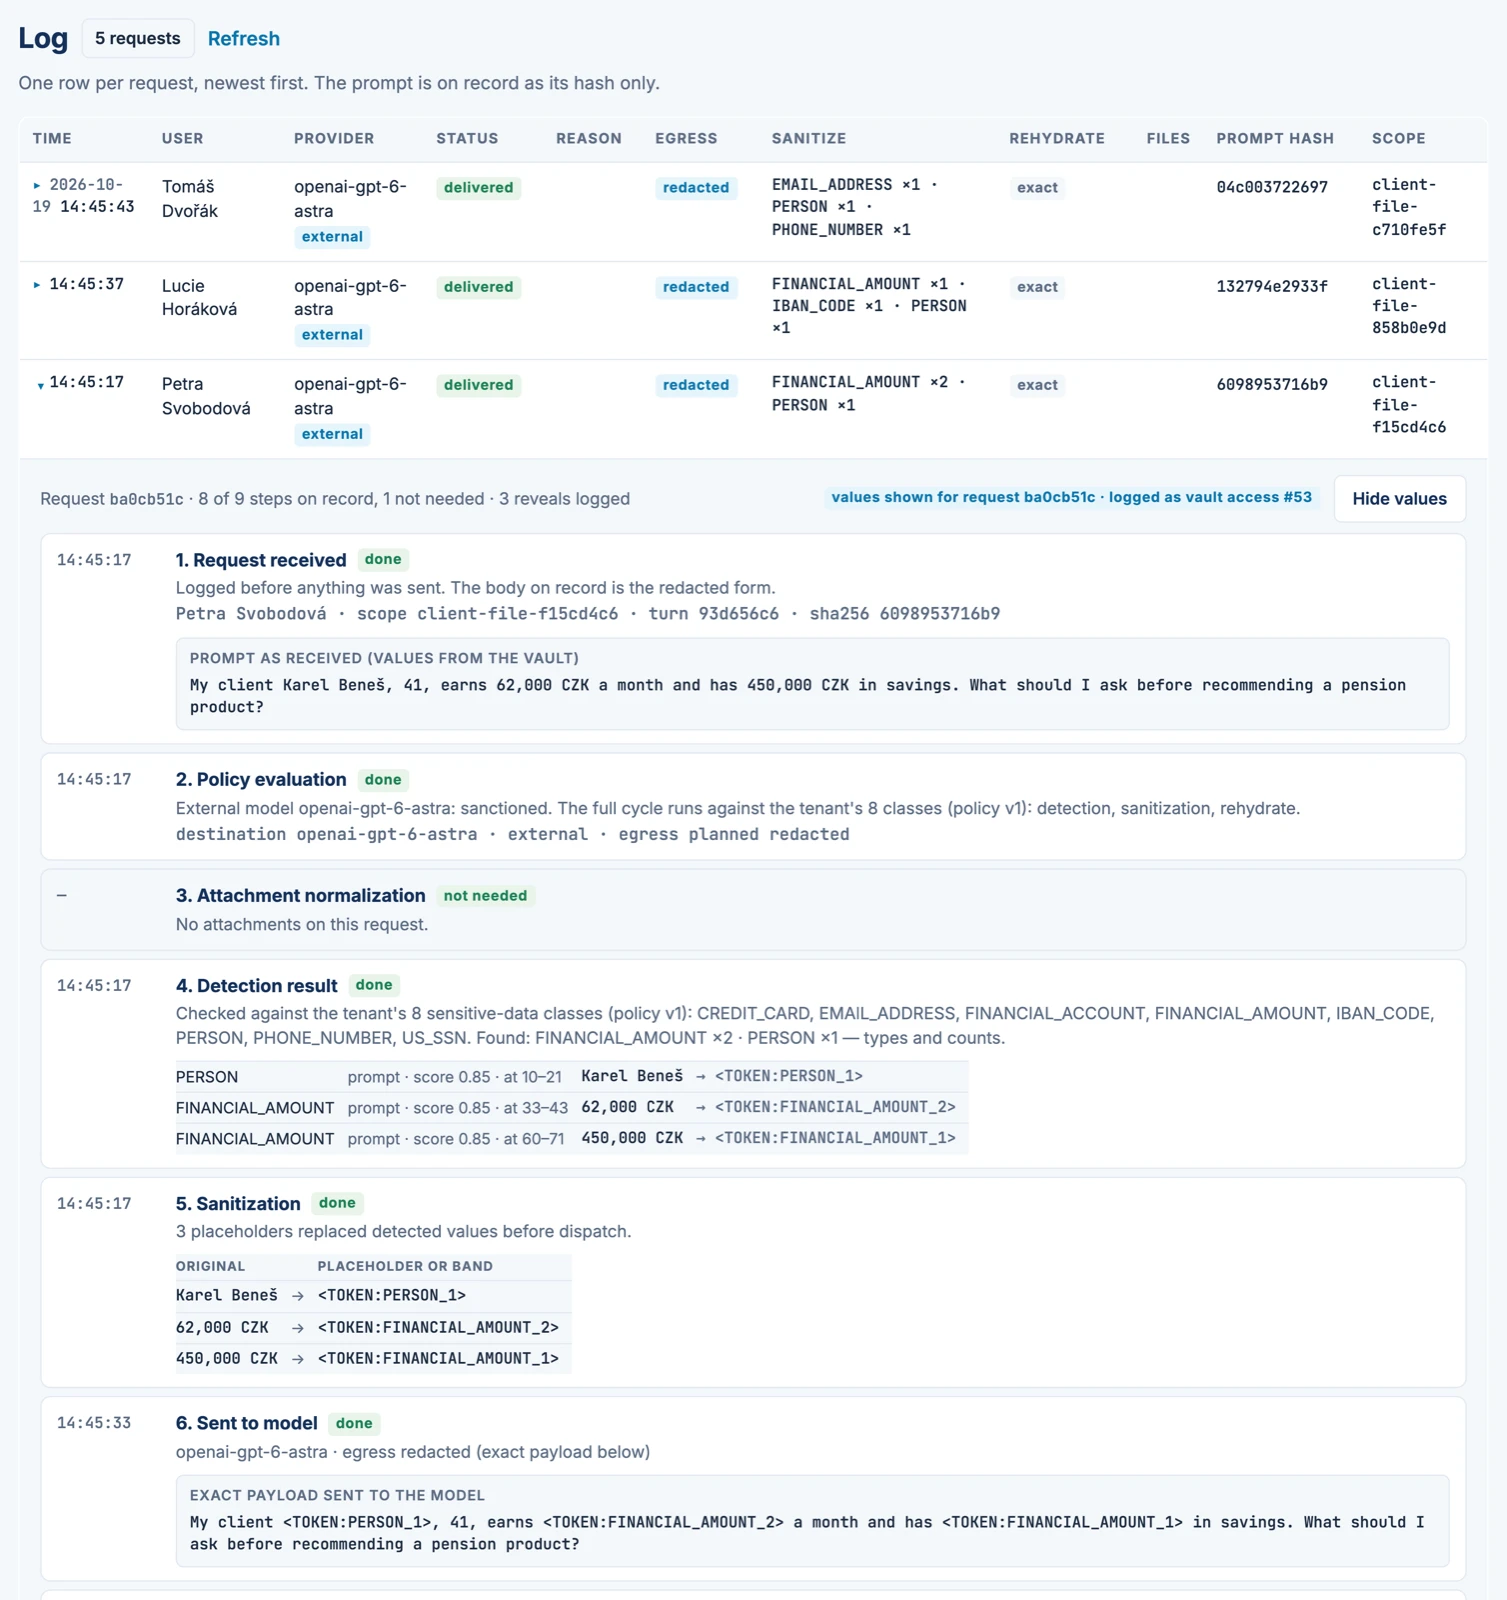
This is the compliance log of the ABOS gateway, running on demo data for a fictional broker network. One request is opened step by step: the prompt as the broker typed it, what was detected, which placeholder replaced each value, and the exact text that went to the model.
Why now
The rules differ between the EU and the US. The question they put to the company is the same.
European Union
Since Oct 2024
Cyber duties reach the mid-market and its supply chain.
17 Jan 2025
Every external AI provider is an ICT third party.
Aug 2025 to Dec 2027
Logging and human-oversight duties arrive in steps, most of them for high-risk uses.
United States
Nov 2025
Supervision of AI use and the accuracy of AI claims, named for advisers.
2026
Keep prompt and output logs, and supervise AI like any other communication.
3 Jun 2026
Customer-data safeguards and incident duties now bind the small firm.
Model vendors will solve their own liability. Never your audit obligation.
EU: Directive (EU) 2022/2555; Regulation (EU) 2022/2554; Regulation (EU) 2024/1689 as amended by Regulation (EU) 2026/1744. US: SEC Division of Examinations, 2026 examination priorities; FINRA 2026 Annual Regulatory Oversight Report; Regulation S-P amendments, compliance date for smaller entities 3 Jun 2026.
Your security stack
Security tools reduce risk. ABOS helps you demonstrate compliance.
Security gateways
ABOS
First pilot
We start with financial intermediaries in Czechia and Slovakia and are selecting our first pilot network.
If your company has to account for its use of AI to a regulator, an auditor or a customer, get in touch. We will show you the gateway running on your own kind of requests.
Team
Business
Six years as CPO in a regulated environment, building a digital bank from scratch to multi-country operations. 3× founder, 2 exits.
Technology
29 years in technology. Two decades of enterprise architecture at Amdocs and BNP Paribas. Now CIO for banking and fintech ventures.